
Speakers
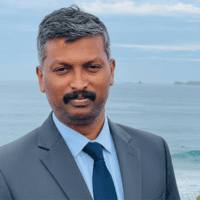
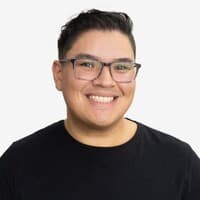
Santhoshkumar Anandakrishnan & Thiago Shimada Ramos
Skyline Technology Aus Pty ltd · EnclaveAI Studio
About
Santhoshkumar Anandakrishnan
Lead Cloud Architect · Skyline Technology Aus Pty ltd
IT professional with 19 years of dedicated experience in Cloud & Infrastructure with globally reputed organisations, backed up by a bachelor's degree in computer science engineering. I specialise in Infrastructure, mainly focusing on public & hybrid cloud, and I work extensively on designing and implementing cloud models that host Business solutions. I hold a Dual MVP from Microsoft for Azure networking and Cloud Security.
Thiago Shimada Ramos
Sovereign AI & Platform Architect · EnclaveAI Studio
I've been navigating the tech world for over a decade. My journey has taken me from Brazil to Japan and now Australia, exposing me to diverse perspectives and approaches to problem-solving. I'm fascinated by the intersection of strategy and technology. When I'm not immersed in Kubernetes (I'm a Kubestronaut!), you'll often find me playing Go or solving Rubik's cubes. My love for Go also sparks my interest in AI, especially the advancements made by AlphaGo.
Session
Securing Azure Kubernetes Service (AKS): Network Policies, Private Clusters & Pod Security
TalkAKS security is often treated as an extension of general Azure network security. Still, Kubernetes networking has its own model, its own failure modes, and its own set of tools — and getting it wrong can undermine every other security control in the environment. This advanced session is built for platform and security engineers who need a comprehensive understanding of securing AKS networking. We'll start by comparing AKS networking models — kubenet, Azure CNI, and CNI Overlay — and the security and scalability trade-offs of each. From there, we dive into Kubernetes Network Policies, comparing Azure's native Network Policy Manager with Calico, and showing how to enforce pod-to-pod and namespace-level segmentation that mirrors the micro-segmentation principles used at the VNet layer. We'll cover private AKS cluster architecture in depth, including how API server access works when the control plane has no public endpoint, and the DNS considerations that come with it. The session also addresses identity: comparing Workload Identity (the modern, recommended approach) against legacy pod-managed identities, and why this choice matters for both security and operational simplicity. A demo session with cluster security settings.
Speaking at
- View event →
Cloud Native AI Summit — Melbourne
October 28–29, 2026